HomeAuto Beijing Firm Integrity Technology Group Hacked Government Email, Built Third-Party Portal
Beijing Firm Integrity Technology Group Hacked Government Email, Built Third-Party Portal
October 10, 2026:
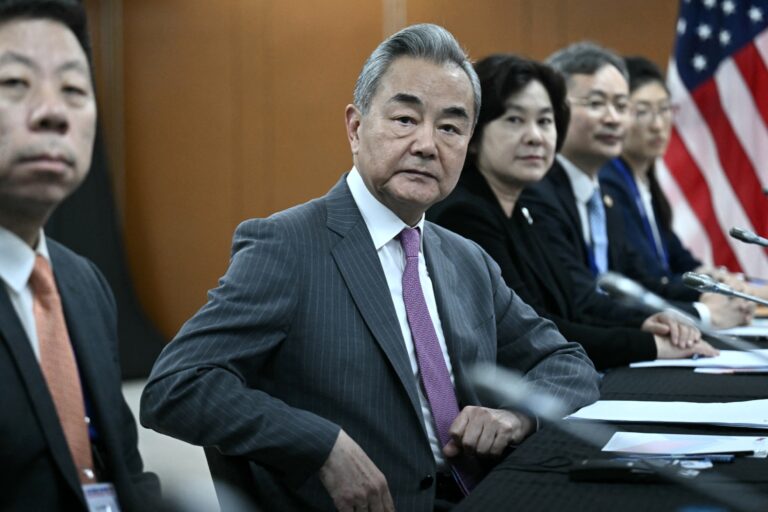
China’s Foreign Minister Wang Yi (C) looks on during a bilateral meeting with US Secretary of State Marco Rubio on the sidelines of the Association of Southeast Asian Nations (ASEAN) Foreign Ministers’ Meeting in Pasay, Metro Manila on July 22, 2026. Brendan SMIALOWSKI/POOL / AFP via Getty Images
For at least five years, actors enabled by a Beijing-based cybersecurity company broke into government agencies, law enforcement bodies, hospitals, and religious institutions across three continents — and then did something more alarming than deleting what they found: they built a custom web application that let unidentified third parties browse the stolen inboxes on demand, querying any victim’s mailbox by passing arguments through a URL. Access to that portal, in at least some cases, was restricted to IP addresses from Xiamen, China.
On October 8, 2026, the FBI and cybersecurity agencies from six allied nations issued a formal joint advisory AA26-281A identifying Integrity Technology Group — a Shanghai Stock Exchange-listed company already under US, UK, and EU sanctions — as the commercial entity that enabled the campaign. The advisory is co-signed by CISA, the NSA, the UK’s National Cyber Security Centre, Australia’s ASD Cyber Security Centre, the Canadian Centre for Cyber Security, Japan’s National Police Agency and National Cybersecurity Incident Response Office, New Zealand’s National Cyber Security Centre, and Spain’s Centro Nacional de Inteligencia. It represents one of the broadest coordinated attributions against a named Chinese commercial entity in recent memory.
Who Is Integrity Technology Group?
Integrity Technology Group — also known as Integrity Tech, and formerly Beijing Integrity Technology Group (BITG) — is a for-profit company incorporated in Beijing. The advisory describes it as a company that acquires or builds cyber tools for use and sale, hosts supporting infrastructure, and facilitates the compromise of networks across global victim organizations.
The company is no stranger to Western government action. The US Treasury Department’s Office of Foreign Assets Control sanctioned Integrity Tech on January 3, 2025, for its role in multiple computer intrusion incidents against US victims, freezing its US-reachable assets and prohibiting US persons from transacting with it. The UK’s Foreign, Commonwealth and Development Office followed with its own cyber financial sanctions on December 9, 2025, designating the company under the UK’s cyber financial sanctions regime for controlling and managing a covert cyber network and providing technical assistance for cyberattacks, including against UK public sector IT systems. The European Union added Integrity Tech to its sanctions list in March 2026.
The company’s profile first rose in the West in September 2024, when the FBI disrupted the Raptor Train botnet — a network of more than 200,000 compromised routers, IP cameras, NAS servers, and other consumer devices that the US Justice Department attributed to Integrity Technology Group’s control. Researchers at Lumen’s Black Lotus Labs had named and publicly documented the botnet, calling it one of the largest China-linked IoT botnets ever discovered.
Then-FBI Director Christopher Wray noted in 2024 that the company’s chairman had “publicly admitted that for years his company has collected intelligence and performed reconnaissance for Chinese government security agencies.”
Integrity Technology Group rejected the US accusations at the time of the January 2025 sanctions, telling the Shanghai Stock Exchange that the US action had no factual basis. A Chinese Foreign Ministry spokesperson said China “firmly opposed” the move.
Five Years of Stolen Government Email
The new advisory goes beyond the botnet disruption. It details how threat actors enabled by Integrity Tech systematically broke into networks and built a sustained email theft operation that has been running since at least mid-January 2021 — with indicators of compromise in the advisory’s appendices stretching as far back as 2016.
Confirmed victims include government organizations, law enforcement agencies, healthcare systems, and religious institutions in Southeast Asia. Additional targeting covered US critical infrastructure sectors including government services, critical manufacturing, healthcare, and IT, as well as US law enforcement, education institutions, and religious organizations. Targets were also identified in Africa and North America.
The advisory does not name specific victim organizations — standard practice for government attributions of this kind.
What the Portal Does: Stolen Inboxes, Searchable on Demand
The most operationally significant element of the advisory is not the intrusion itself — it is what happened after the intrusion. The threat actors built a custom web application that provides third-party access to stolen email content, allowing authorized users to query any mailbox via URL, passing account identifiers as arguments directly in the address. The advisory does not identify who those third parties are.
In some observed incidents, access to the stolen data was restricted to IP addresses from Xiamen, China.
This architecture is meaningfully different from conventional email exfiltration, in which stolen data is copied to attacker-controlled storage and read statically. A URL-queryable interface designed for ongoing third-party access is closer in structure to a surveillance product — a persistent intelligence service built on a continuously updated pool of stolen correspondence. The advisory does not state whether the portal has been taken down, and organizations whose email may have been stolen cannot assume that past access has ended simply because intrusion activity was detected.
How They Got In: Reconnaissance to Initial Access
The advisory provides granular technical detail on the threat actors’ methods, drawing on evidence from multiple FBI cyber investigations.
Reconnaissance begins with open-source scanning tools available on GitHub — Nmap, masscan, WPScan, BBScan, dirsearch, Fscan, and others — focused on ports 21 (FTP), 22 (SSH), 53 (DNS), 80 (HTTP), 443 (HTTPS), and 1080 (SOCKS). The advisory notes that the choice of publicly available tools suggests the actors tend to look for more vulnerable targets rather than hardened ones, preferring low-hanging fruit over custom exploits against well-defended networks.
Since at least 2017, the actors have also used MicroScan — a custom Python-based web application containing more than 1,300 penetration testing scripts targeting specific software vulnerabilities. The scripts have been used against services including OpenSSL, Oracle WebLogic Server, WordPress, Juniper ScreenOS, Jenkins, and Apache Struts. The UK’s NCSC stated in the NCSC’s advisory press release that the hackers are “uniquely using AI tools, such as automated scanning,” though the advisory’s body does not elaborate further on AI usage.
Initial access uses command-line exploit code written in Python and Go, along with cross-site scripting attacks. The FBI recovered one XSS payload that modifies a vulnerable webpage to display fake username and password fields; when a victim enters credentials, the page serves a download link for a password-protected ZIP file. That archive contains live700_v1.exe and DiagTrack.exe malware — the second sharing its name with a legitimate Windows diagnostic service — and establishes encrypted communications with a domain the FBI attributes to Integrity Tech. The malware appears designed to target email data.
For cloud and on-premise email environments, the actors use EBurst — an open-source Python tool for password spraying and credential guessing against Microsoft 365 and Exchange. EBurst cycles through ten Exchange authentication endpoints — ECP, EWS, OAB, OWA, RPC, MAPI, and Microsoft-Server-ActiveSync among them — making it capable of testing every available authentication endpoint in sequence. An organization that locked down Outlook Web App alone still left nine other doors open. The advisory explicitly urges defenders to cover all ten interfaces.
Eight known vulnerabilities are listed as successfully exploited in the campaign, including flaws in GNU Bash (CVE-2014-6278), ProFTPD (CVE-2015-3306), ISC BIND (CVE-2015-5477), Apache Struts (CVE-2016-3081), Pulse Connect Secure (CVE-2019-11510), GitLab (CVE-2021-22205), ONLYOFFICE Document Server (CVE-2021-3199), and Strapi (CVE-2023-22894). Five of the eight were added to CISA’s KEV catalog concurrently with the advisory’s release — creating an immediate patching obligation for US federal agencies under Binding Operational Directive 22-01.
How Did Hackers Maintain Access and Steal Email at Scale?
Persistence relies on SoftEther, a legitimate SoftEther VPN client, installed on compromised devices. Because SoftEther is real, widely used software, it is less likely to be flagged by endpoint security tools. The installers were typically renamed conhost.exe or dllhost.exe — process names that match legitimate Windows components — and configured to reconnect automatically at startup, ensuring continued access even after reboots or partial remediation attempts.
Credential theft was accomplished through DC.exe, a tool that uses the DCSync credential extraction technique to silently impersonate a domain controller’s replication process. Rather than physically accessing a domain controller or logging into individual accounts, DCSync requests password data from the DC as if conducting legitimate Active Directory synchronization — extracting account credentials, group memberships, and trust relationships for an entire domain in a single operation. The resulting credential dump provided access to email accounts across the compromised network.
Email collection used two mechanisms. The first is Curlc4.txt — a Curlc4.txt PHP email script that interfaces with Microsoft’s Exchange Web Services API to continuously collect email, calendars, and contacts. The bot compressed stolen mail before uploading it to a remote server — in some cases encrypting it with RC4 or AES-128-CBC — using natcloudservice[.]com as its primary command-and-control domain. The second is office-cli, a command-line tool that used stored OAuth credentials (client ID, tenant ID, and client secret) to continuously access Microsoft 365 accounts and pull mail across configurable time periods. Because office-cli uses the same application-access methods as legitimate Microsoft 365 integrations, it was designed to appear indistinguishable from authorized software.
What Organizations Should Do Now
The seven-nation coalition’s advisory recommendations urge defenders to take the following steps immediately:
Disable unused services and ports, including remote access protocols and file-sharing services that are not operationally required.
Sanitize web application inputs to block the XSS injection used in initial-access phishing.
Require multifactor authentication for all services, especially webmail, VPNs, and accounts touching critical systems. MFA is explicitly called out as the single most effective mitigation against EBurst-style password spraying.
Watch for unexpected Active Directory replication requests — the primary detection indicator for DCSync activity via DC.exe.
Audit cloud accounts for connected applications with access to email and files. office-cli’s use of legitimate OAuth credentials means it will appear as an authorized app in Microsoft 365’s connected-applications list.
Review web application logs for scanning and enumeration patterns consistent with MicroScan and EBurst reconnaissance.
Apply patches for the eight CVEs in the advisory, and replace any end-of-life products that cannot be patched.
For organizations that believe they may already be compromised, the advisory recommends isolating affected hosts and conducting threat-hunting before eviction — to avoid alerting the actors prematurely and losing the ability to map the full extent of the intrusion. Organizations should also follow national reporting requirements for their respective jurisdictions.
The advisory’s 39-page IOC appendix — containing domains, IP addresses, and file hashes, some dating to 2016 — is available from IC3.gov in both STIX XML and STIX JSON formats. The authoring agencies recommend checking the IOCs against historical logs before blocking, because some “last seen” dates in the tables may not reflect the most recent activity on record. Ten IP addresses from the advisory also appeared in the September 2024 Raptor Train advisory, where they were listed as command-and-control servers.
Why Japan and Spain Make This Advisory Different
The October 8, 2026 advisory is notable on several counts beyond its technical detail.
It follows a multi-year escalation against Integrity Technology Group: botnet disruption in September 2024, US Treasury sanctions in January 2025, UK sanctions in December 2025, EU sanctions in March 2026, and now a seven-nation joint public attribution of a separate, ongoing email theft campaign. The company has continued operating through each escalating measure.
The participation of Japan and Spain alongside the traditional Five Eyes partners (US, UK, Australia, Canada, and New Zealand) signals a broadening coalition willing to put their names to China-attribution advisories — a diplomatically significant step, the NCSC press release confirmed. Japan has participated in prior “Five Eyes Plus” cyber cooperation on North Korea, but its involvement in this China-attribution advisory carries additional weight. Spain’s participation via the CNI is particularly notable: Spain has not been prominently involved in prior China-specific cyber attributions, and its inclusion suggests that Western Europe is increasingly willing to join formal attribution actions against Chinese commercial entities.
The advisory also underscores a recurring structural feature of documented Chinese state cyber operations: the use of private-sector intermediaries — companies like Integrity Tech that sit between the government and the intrusion activity — to provide a layer of deniability. The advisory describes Integrity Tech as a for-profit company with government links whose employees build tools “for use and sale,” host infrastructure, and facilitate network compromises. This contractor model has been documented in parallel cases involving other Chinese cybersecurity firms, including I-Soon (whose internal documents leaked in 2024) and companies linked by Recorded Future APT3 research to APT3 activity. Wray’s attribution of the chairman’s admitted intelligence collection activities confirms that in Integrity Tech’s case, the contractor relationship was not merely structural but operationally admitted.
The threat actors’ methods are described as consistent with activity tracked publicly as Flax Typhoon, Ethereal Panda, and RedJuliett — overlapping designations used by different security firms for a cluster of Chinese state-linked intrusion activity. The advisory cautions that these labels may not map one-to-one to US government tracking, and that the same actors may also conduct activity unrelated to Integrity Tech.
Frequently Asked Questions
What is the stolen email portal described in the advisory, and could it still be active?
The advisory describes a custom web application built by Integrity Technology Group-linked actors that allows authorized third parties to access stolen email from victim organizations. Users can call up a specific mailbox’s contents by passing account identifiers as URL arguments — a design that functions more like a searchable intelligence product than a conventional data dump. In at least some documented cases, access was restricted to IP addresses originating from Xiamen, China. The advisory does not state that the portal has been taken down, and organizations that believe their email may have been stolen cannot assume that third-party access to that correspondence has ended.
What is the Flax Typhoon connection, and why are three names used for the same hackers?
The advisory says the threat actors’ methods are “consistent with” activity tracked as Flax Typhoon, Ethereal Panda, and RedJuliett — three names applied by different security vendors (Microsoft, CrowdStrike, and Recorded Future, respectively) to overlapping clusters of Chinese state-linked intrusion activity. Different firms observe different subsets of operations and apply their own naming conventions, so the same group can accumulate multiple designations. The advisory explicitly cautions that these names may not map one-to-one to US government tracking and that the same actors may also conduct unrelated operations. Flax Typhoon was first publicly described by Microsoft in 2023 as targeting Taiwan-based organizations; Recorded Future’s RedJuliett research documented similar targeting of Taiwanese government, research, and critical infrastructure.
Which specific CVEs were exploited, and do I need to patch them now?
The advisory lists eight CVEs exploited in the campaign: CVE-2014-6278 (GNU Bash), CVE-2015-3306 (ProFTPD), CVE-2015-5477 (ISC BIND), CVE-2016-3081 (Apache Struts with Dynamic Method Invocation enabled), CVE-2019-11510 (Pulse Connect Secure), CVE-2021-22205 (GitLab), CVE-2021-3199 (ONLYOFFICE when JWT is used), and CVE-2023-22894 (Strapi). Five of these were added to CISA’s Known Exploited Vulnerabilities catalog concurrently with the advisory — which means US federal agencies are legally required under Binding Operational Directive 22-01 to patch them within the KEV’s required timeframe. Private-sector organizations that have not already patched end-of-life products affected by these vulnerabilities should treat them as urgent, particularly the older CVEs, which may indicate legacy systems that have been unpatched for years.
How does China’s own law require companies like Integrity Tech to work with the government?
China’s National Intelligence Law (2017), Article 7, requires that all Chinese organizations and citizens “shall support, assist, and cooperate with national intelligence work” upon request. This is not a discretionary provision — it is a legal obligation that applies to every company incorporated under Chinese law, including Integrity Tech, regardless of the company’s publicly stated commercial purpose, its denial of government ties, or the location of its servers. China’s Cybersecurity Law (2017) and Data Security Law (2021) add further provisions requiring data localization and government access. These obligations exist as a fixed structural condition of operating under Chinese jurisdiction. They do not depend on whether a given company has been observed complying — they mean that any such company can be compelled to comply. Then-FBI Director Christopher Wray’s 2024 statement that the company’s chairman publicly admitted collecting intelligence for Chinese government security agencies confirmed that in Integrity Tech’s case, that legal framework was operationally exercised, not merely theoretical.
The full joint advisory, including the complete indicators of compromise in both STIX XML and STIX JSON formats, is available from the FBI’s IC3 advisory portal.